G'day
I'm Deeno.
Some people call me the Space Cowboy a Joker · Smoker · Midnight Toker
Senior Product Security Engineer previously AppSec · Pentest · Software Eng
Usually found in a State Park, planning another trip to Japan, or
convincing someone into a day out because I'm bored.
I also do computery and security things as a job.
Product security: vulnerability management, security tooling at scale, design and code reviews, and incident response. Built software first, broke it professionally second, and now help engineers fix it properly.
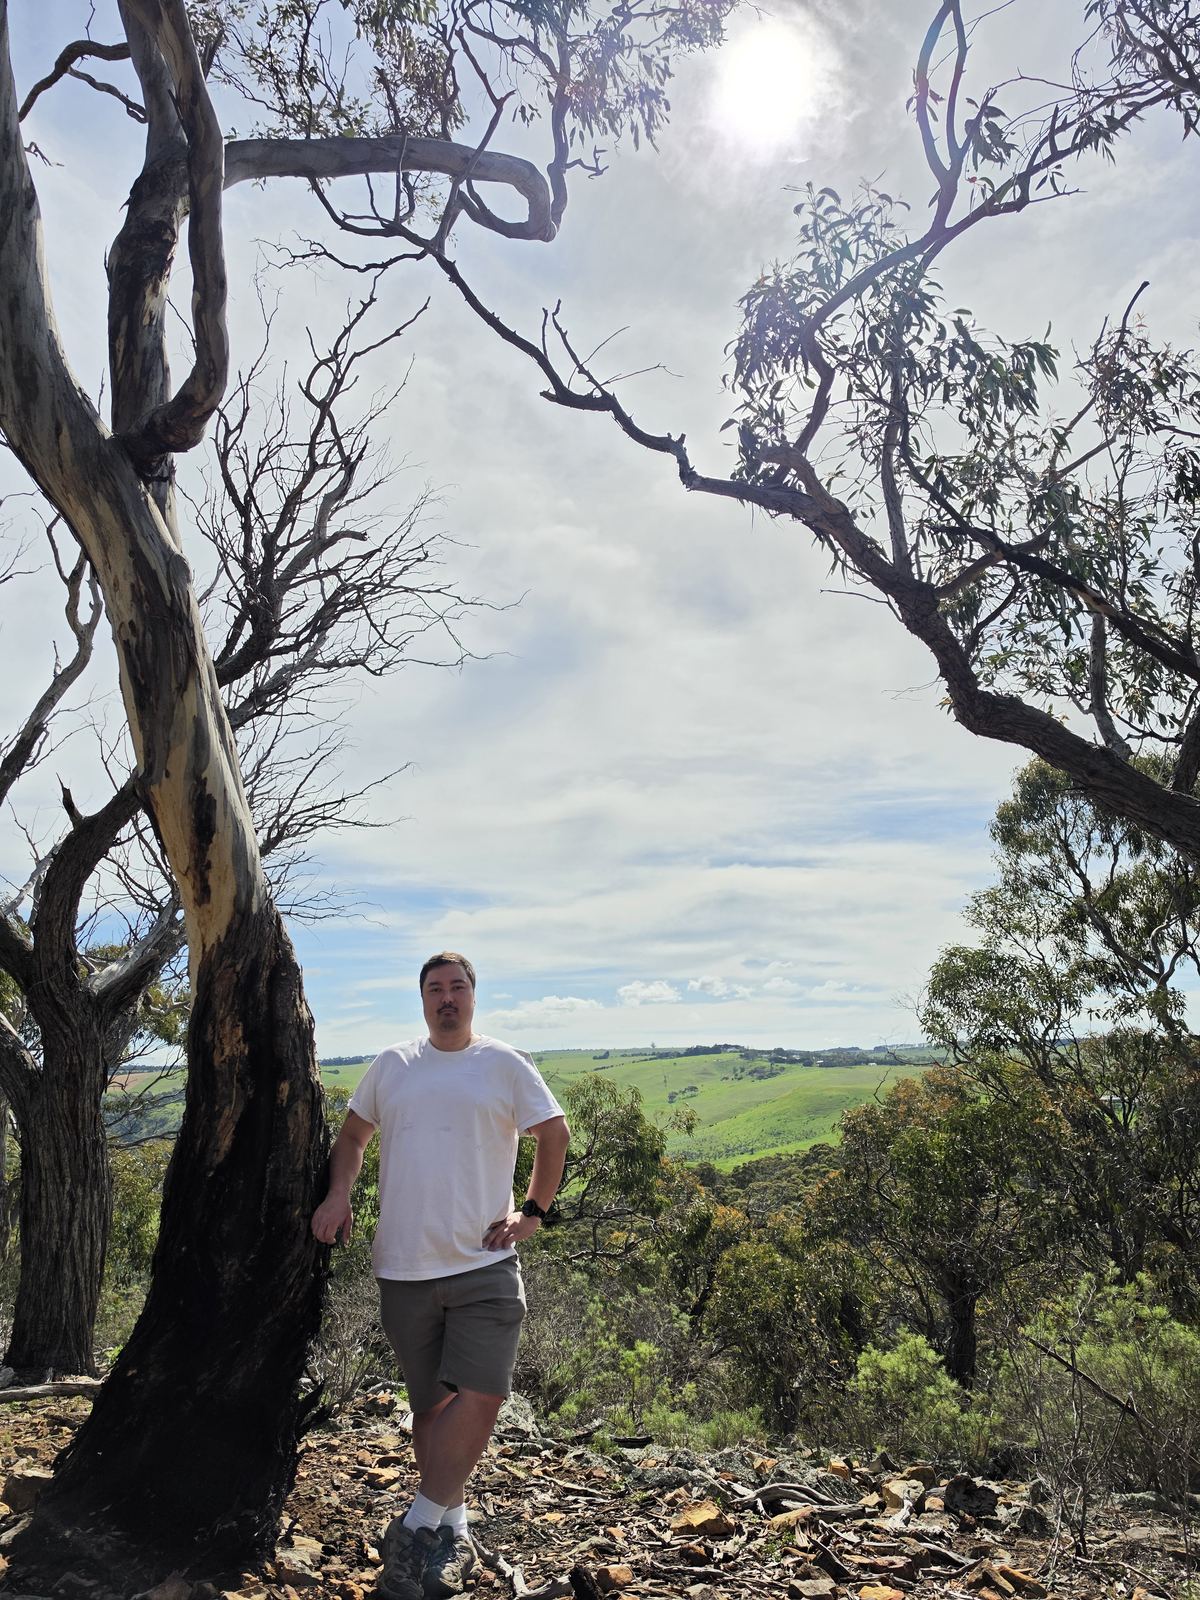
The trail so far
Every career has an elevation profile. Mine started at the bottom of the stack and has mostly been uphill since (the good kind).
-
01
Trailhead
Software Engineer
Learnt from some amazing people, building software in a high safety environment with lots of requirements. Oh how I miss when people actually had to specify what their apps did.
-
02
The scramble
Penetration Tester
Got pretty good at breaking things, realising how insecure most orgs actually are. Surely no one is vulnerable to EternalBlue anymore?
-
03
The ridge
AppSec Engineer
Started out as onboarding engineering teams to the security tools, and seeing how the vulnerabilities that I would have identified in pentests actually get fixed.
-
04
Summit (for now)
Product Security Engineer
This is where things get insane because prodsec was a bit of everything. All the stuff from appsec, plus incident handling, WAF management, security automations, tooling, scheduling pentests, and don't even get me started on AI security.
What I do on weekdays
"Product security" means something different everywhere. Here's what it looks like for me.
$ whoami --history
2018  software engineer
2022  offensive security consultant
2024  product security engineer

$ ls ~/certs
OSCP  CPTS  CWES  CRTO  CRT  CPSA

$ cat ~/cves.txt
CVE-2024-41703  librechat
CVE-2024-41704  librechat

$ cat philosophy.txt
fix root causes, not just tickets.
explain risk in plain english.

$
-
Vulnerability management
Getting critical and high findings fixed faster, plus running bug bounty programmes and triaging what comes in.
-
Security tooling at scale
Rolling out SAST and cloud security scanning across a lot of repos, and onboarding teams to security checks in CI/CD.
-
Design & code review
Manual and AI-assisted reviews of high-risk systems, architecture consults, and scoping and running pentests before features ship.
-
Incidents & WAF
Escalation point for security incidents, supply chain ones included. Plus WAF tuning, managed as code.
-
Security Champions
Running a champions programme with regular sessions and secure-development training. Security you ask early, not hide things from.
-
AI in the loop
Building AI-assisted threat modelling workflows, and Claude Code skills that automate away the tedious bits of security work.
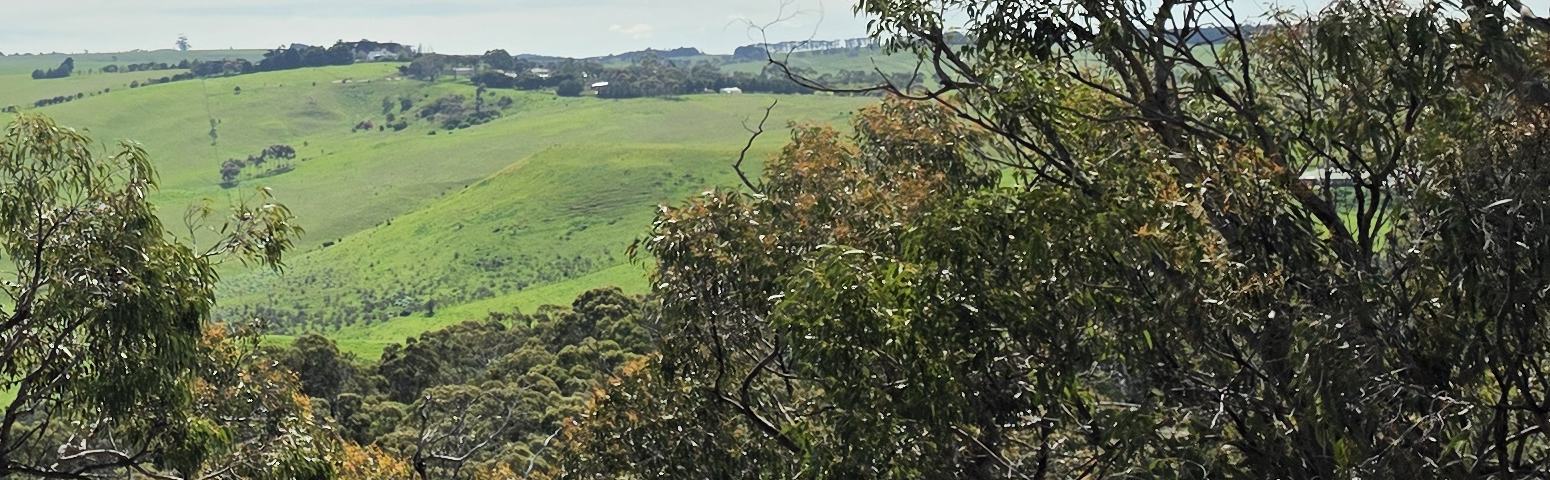
the view from the top
Every hike is a long negotiation for a view like this.
Off the clock
I have literally the same hobbies as literally everyone else on the planet. I hope none of these come as a surprise to you.
完走! Rally complete. You've officially met weekend me.
Sign the trail register
Want to talk threat models, product security, or how to make security teams less scary? Or need trail recommendations and Japan itinerary opinions? Both are welcome.